Cybersecurity Training That Sticks: Lessons, Not Lectures
January 5th, 2027
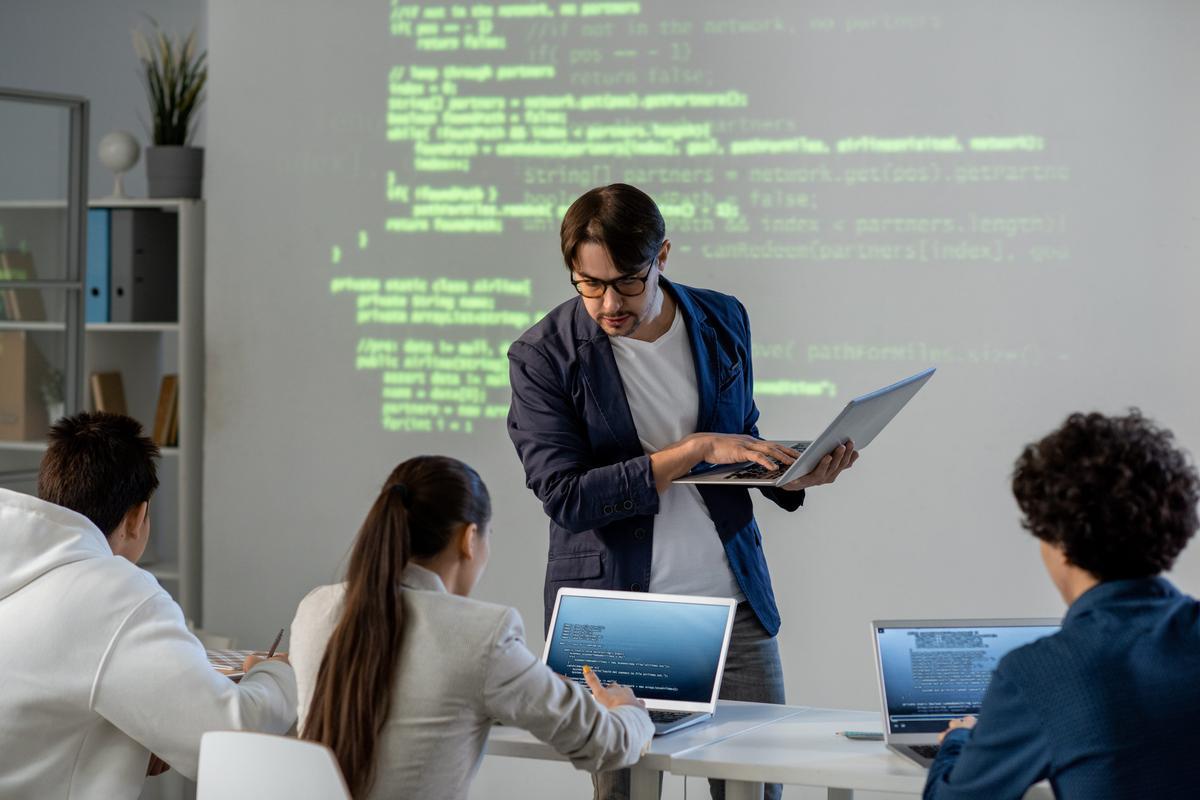
Every year the training module gets assigned, everyone clicks through the slides, and the completion report lands in a folder. Six weeks later an employee approves a suspicious MFA prompt and the report means nothing. Completion was never the goal. Behavior was.
Employees are not failing security training because the topic is too hard. Most programs fail because they teach awareness instead of action. People leave knowing that phishing exists, but not knowing what to do when a message arrives at 4:45 on a Friday and looks exactly like the vendor invoice they were expecting.
Training that sticks is built around a small set of repeatable behaviors, practiced often enough to survive a busy day. It respects the employee's time, uses examples from the work they actually do, and measures whether the right action happened when it mattered.
Why Completion Rates Mislead
A completion rate measures whether someone opened a course, not whether they learned anything. The number is easy to produce and easy to report upward, which is exactly why it survives. It also creates a false sense of protection.
Attackers do not send a quiz. They send a message that fits the employee's role, references a real project, and asks for something ordinary. The employee who passed last year's module with a perfect score may still wire a payment to a fraudulent account if no one ever taught the verification step as a habit.
Replace completion as the primary measure with behaviors you can observe. How quickly do employees report suspicious messages? How often do they verify a payment change by phone? How many reuse a password that appears in a breach? Those numbers tell you whether the program is working.
Teach Behaviors, Not Trivia
A useful curriculum fits on one page. If employees remember five things a year from now, choose those five carefully and repeat them until they are automatic.
Pause and Verify Before Acting
The core habit is a short pause before any action that involves money, credentials, or data. Teach employees to check the sender's actual address, question urgency, and confirm unusual requests through a second channel they already trust.
Make the second channel specific. "Call the person" is vague. "Call the number in the vendor record, not the number in the email" is a behavior. "Use the chat thread you already had open" is a behavior. Specific steps survive pressure; general advice does not.
Report Without Fear
Employees hide mistakes when reporting leads to blame. That silence is more dangerous than the mistake itself, because a reported message can be removed from every inbox in minutes.
Give employees one obvious way to report, confirm receipt, and tell them what happened. When someone reports a real phishing attempt, say so. When simulations are reported, count that as success rather than failure.
Protect Accounts by Default
Teach the account habits that prevent most credential theft: use the company password manager, accept MFA prompts only for logins you started, and never share a one-time code with anyone who calls or messages.
The last point deserves repetition. Help desk impersonation is common because it works. No legitimate IT person needs an employee's password or MFA code, and employees should hear that from leadership, not only from a slide.
Know What to Do After a Mistake
People who know the recovery path report faster. Tell employees exactly what happens after a click: call the service desk, do not delete the message, do not try to fix it alone. The speed of disclosure limits the damage.
Formats That Stick
Short Sessions, Spaced Out
A 45-minute annual lecture is forgotten by lunch. Ten-minute sessions once a month, with the same core message repeated in different scenarios, produce better retention and less resentment.
Spacing also gives employees time to practice between sessions. A short lesson on payment verification is more useful in March when the finance team has a real invoice cycle to apply it to than in a generic January compliance push.
Real Examples and Simulations
Use messages that resemble what your employees actually receive. Industry-specific lures, vendor impersonation, payroll notices, and shipping updates work better than generic "you have won a prize" examples that nobody would believe.
Simulations should teach, not trap. Send them at a realistic pace, keep the fake login pages clearly labeled after the click, and follow every simulation with a short explanation of the cue that was missed. Punishing clicks teaches people to hide, not to verify.
Role-Specific Scenarios
Finance needs payment fraud and invoice manipulation. HR needs payroll diversion and fake candidate resumes. Executives need impersonation and travel scams. Service desk staff need identity verification and escalation procedures.
Role-specific content feels relevant because it is. Employees pay more attention when the example could plausibly land in their inbox that week.
Practice, Not Just Content
People learn procedures by doing them. Run a short drill where an employee receives a suspicious request and has to find the right phone number, confirm the request, and report it. The first attempt will be awkward. That is the point.
Measure What Matters
Build a small dashboard with leading and lagging indicators. Leading indicators show whether the program is reaching people. Lagging indicators show whether behavior changed.
- Reporting rate: the share of simulated phishing messages employees report
- Time to report: how quickly a suspicious message reaches the security team
- Repeat click rate: how many employees click more than once across simulations
- Verification compliance: spot checks showing payment changes confirmed by phone
- Password hygiene: password manager adoption and MFA enrollment
Review the numbers quarterly and change one thing at a time. A reporting rate that rises while click rates fall is a good sign. A completion rate that rises while nothing else moves is not.
Build a 90-Day Plan
Start with a baseline. Run one simulation and one short survey to find out what employees currently do. Then pick three behaviors, build short monthly lessons around them, and give managers a one-page guide so they can reinforce the same message in team meetings.
In the second month, add role-specific scenarios for finance, HR, and the service desk. In the third month, review the data and adjust. Keep the program small enough to sustain and specific enough to measure.
Make Security Part of the Job
Training works when it is treated like any other operational skill: practiced, measured, and supported by the tools people use. A verification habit is easier when the phone number is easy to find. Reporting is easier when the button is in every email client. MFA is easier when the prompt explains what is happening.
ATS helps Northern California businesses build cybersecurity programs that combine sensible technical controls with training employees will actually use. If your current program is an annual slideshow, contact our team to build something that changes behavior.
Posted in: Cybersecurity